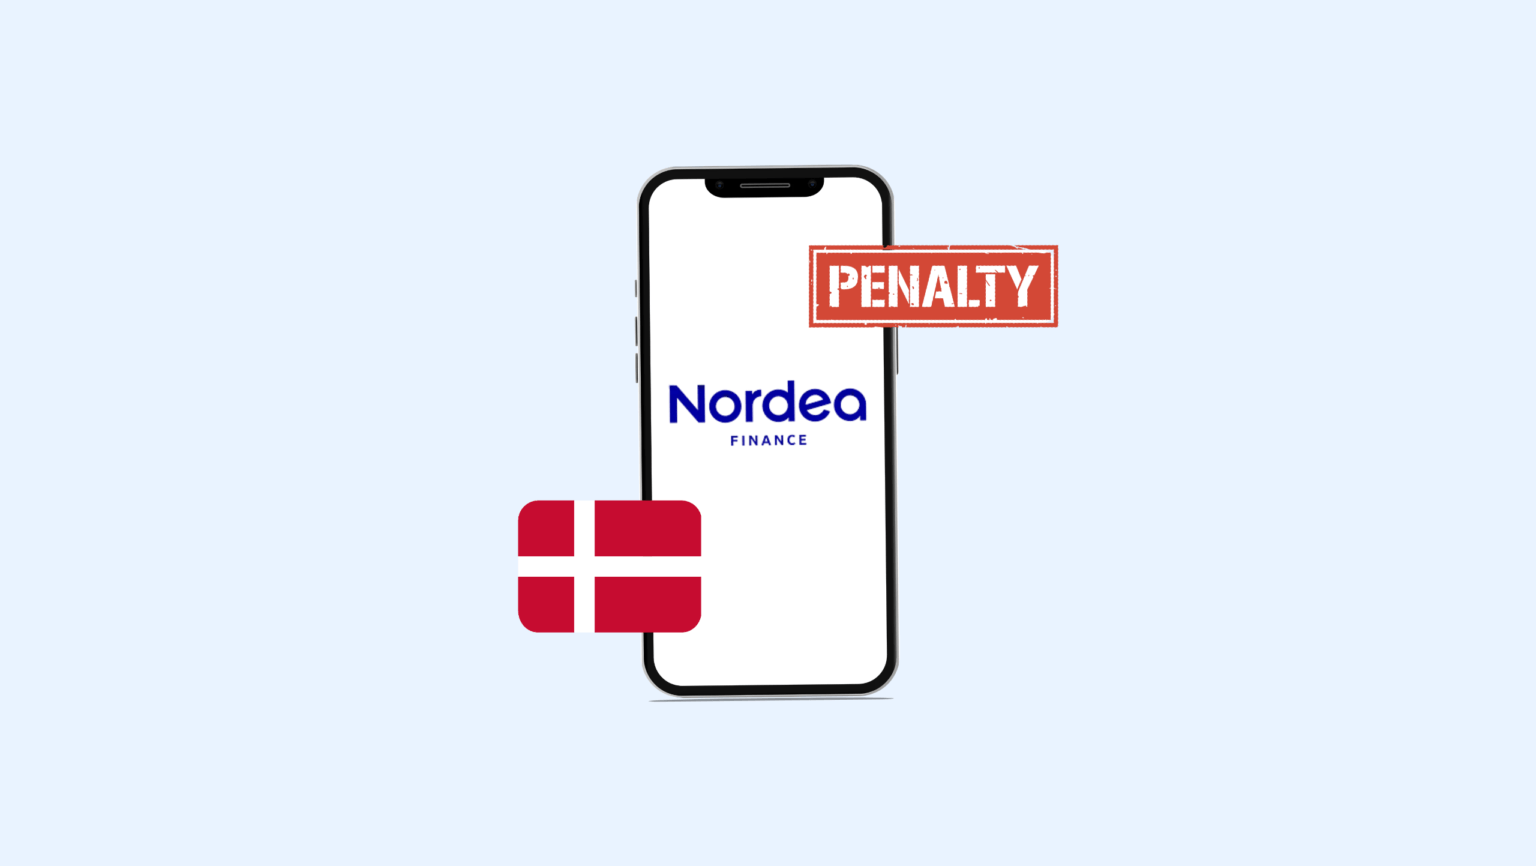
On 9 November 2026, the Copenhagen City Court fined Nordea DKK 155 million (~USD $23 million) for serious violations of Denmark’s Anti-Money Laundering (AML) laws between 2012 and 2015. This ruling followed a decade-long investigation into Nordea’s compliance controls.
Nordea $23 Million Penalty Breakdown
Beginning in July 2024, Denmark’s Special Crime Unit (NSK) formally charged the bank after investigations, alleging it failed to investigate funds linked to Russian customers adequately and ignored red flags about transactions linked to Copenhagen currency exchange offices between 2012 and 2015.
The prosecution sought to penalize the company with an initial 6.6 billion DKK (~USD $988 million), because of the severity of its findings. However, the Danish court agreed to a $23 million penalty after finding the bank guilty on two of the seven formal charges brought by the NSK.
According to the NSK, the alleged AML-related failures included:
- Weak due diligence: The bank failed to perform appropriate customer due diligence on high-risk clients, overlooking red flags such as opaque ownership structures.
- Weak monitoring controls: Nordea lacked the right AML controls to identify and investigate suspicious funds. This led to over DKK 26 billion in suspicious transactions flowing through its systems, some tied to Copenhagen currency exchanges and infamous “laundromat” schemes in Russia and Azerbaijan.
- Failure to report alerts: The bank ignored internal compliance warnings and had major gaps in its processes. This raises concerns about its ability to identify and report high-risk funds or customers to authorities in time.
There’s a difference between whether you could have done something better and whether you have committed a criminal act.
Nordea denies these violations and says it will review the verdict before deciding whether to appeal. The group general counsel at Nordea Denmark, Anders Holkmann, notes, “Our controls and processes 10 years ago could, particularly when viewed from today’s perspective, have been better. But there’s a difference between whether you could have done something better and whether you have committed a criminal act.”
Nordea Bank History of AML Enforcement Action
Nordea is the leading Finland-based financial services company in the Nordics, with major shareholders including BlackRock and Vanguard. In 2025, the company’s operating profit sat at €6.3 billion (~USD $7 billion), with over 30,000 employees operating globally. While the bank invests heavily in risk and compliance management, it is not the first time it has faced regulatory scrutiny.
In 2024, the New York State Department of Financial Services (NYDFS) penalized the bank $35 million for failures to comply with the U.S. Bank Secrecy Act. This fine followed disclosures in the 2016 Panama Papers leak, which exposed several weaknesses in the bank’s AML program. This included failing to apply appropriate due diligence to high-risk banking relationships and funds.
Nordea has had major deficiencies in its work to prevent money laundering.
In 2015, Swedish authorities fined the bank SEK 50 million (~USD $5 million) for systematic compliance failures. This was the highest administrative penalty under Swedish law at that time. Regulators said Nordea had major systematic deficiencies in customer risk assessments, due diligence, transaction monitoring, and internal governance.
Consequently, the regulator notes, “There is a high probability that if people have tried to launder money or finance terrorism that they could have done so without Nordea having been able to detect this.”
Can Banks Avoid Penalties for Previous Compliance Failures?
“Nordea invests over €2 billion on its financial crime prevention infrastructure. Yet, it cannot erase past compliance failures. Today’s regulatory scrutiny depends on yesterday’s decisions,” notes Harry Varatharasan, ComplyCube’s Chief Product Officer.
For regulated financial services, strong AML, Kunden-Due-Diligence (CDD), and risk assessments should not be treated as a switch you can turn on and off at any time. Authorities are increasingly penalizing firms that cannot reliably demonstrate the effectiveness of their compliance infrastructure in identifying emerging financial crime threats:
- Accountability and Oversight: Assign clear ownership of AML functions, with regular senior management review and testing on system effectiveness, emerging risks, and remediation efforts.
- Continuous Risk Assessments: Consistently, securely, and accurately reassess customer risk profiles to strengthen ongoing due diligence and adapt transaction monitoring to newer threats.
- Audit-Ready Recordkeeping: Firms must maintain clear, timestamped audit trails of customer checks, suspicious activity investigations, and corrective actions to demonstrate compliance decisions.
Weitere Neuigkeiten zum Thema Geldwäschebekämpfung finden Sie in ComplyCubes Newsletter „Trust Edition“. Wir beleuchten die neuesten Entwicklungen im Bereich der Identitätsprüfung und der Bekämpfung von Geldwäsche weltweit.